Panic makes for terrible policymaking.
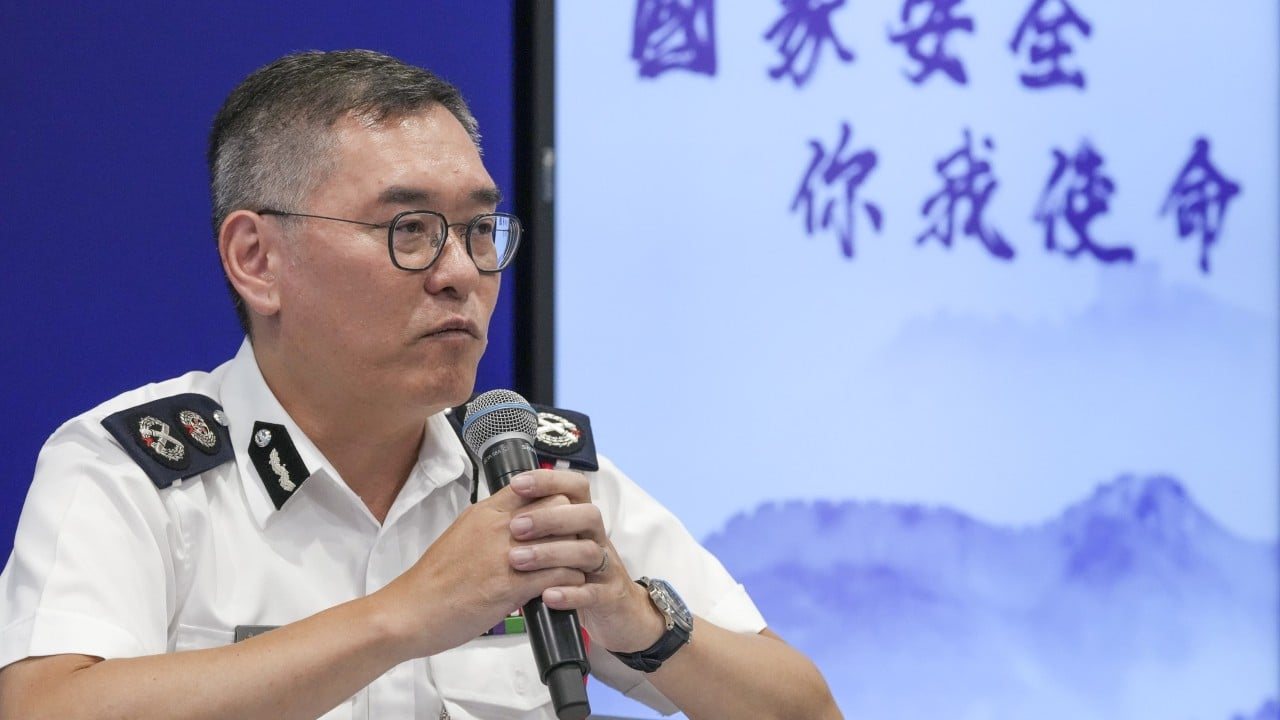
When outgoing Hong Kong deputy police chief Fred Shiu Sing-tak stood up to warn that artificial intelligence represents an unprecedented national security threat, he was doing what bureaucrats do best: projecting human institutional terror onto algorithms that do not care about borders, flags, or state secrets. The lazy consensus in security circles right now is that machine learning models are autonomous weapons factories waiting for a malicious prompt, ready to overthrow states from a basement laptop.
It is a comforting fantasy for people who want to justify larger surveillance budgets and tighter controls over information flow. It is also entirely backwards.
I have spent the last decade watching legacy security agencies trip over their own shoppes trying to regulate software they fundamentally misunderstand. They treat intelligence systems like insurgent cells, imagining a ghost in the machine plotting a coup. Let us strip away the bureaucratic hysteria and look at the actual mechanics of computational risk. The real danger of machine intelligence to national security is not that it will turn rogue and start a war. The real danger is that it will expose just how fragile, antiquated, and easily spoofed traditional state security apparatuses actually are.
The Myth of the Autonomous Threat Actor
The standard narrative goes something like this: a rogue state or a syndicate of hackers deploys an advanced neural network to crack encryption, autonomously coordinate cyber-attacks, and generate deepfakes so convincing they destabilize governments overnight.
This argument collapses under the weight of basic systems engineering.
Large language models and diffusion architectures do not possess agency. They possess math. They do not wake up with an ideological axe to grind against the Hong Kong Special Administrative Region or any other administration. They predict the next token in a sequence based on training distributions compiled from public internet data. When a state official claims that software is a national security threat, they are usually confusing the tool with the human operator wielding it.
Blaming the model for security breaches is like blaming a photocopier for espionage because someone duplicated classified documents.
Consider the obsession with automated cyber-warfare. Security analysts love to talk about self-healing malware and zero-day exploits discovered by neural networks in milliseconds. I have watched defense contractors pitch these sci-fi nightmares to nervous procurement officers while sweating through their collars. The reality in the field is vastly more mundane. Automated scripts have existed for decades. Adding probabilistic token prediction to an exploit script does not turn it into Skynet; it just makes it more expensive to run and prone to hallucinating syntax errors.
Bureaucracy Versus Complexity
Why do senior law enforcement officials keep missing the mark? Because traditional security is built on a command-and-control hierarchy. You have a chain of command, a jurisdictional boundary, and a clear adversary.
Computational systems operate on distributed, decentralized complexity.
When a police deputy chief warns about machine intelligence destabilizing public order, what they are actually admitting is that they can no longer monopolize the narrative. For decades, state security relied on information scarcity. If you controlled the press, the broadcast towers, and the telecom switches, you controlled public stability.
That monopoly is gone. An open-source model running on a rig in a suburban garage can synthesize localized sentiment, translate dialects, and bypass traditional border filters faster than a room full of analysts can draft a memo. The threat to national security is not foreign infiltration via software; it is the democratization of high-level analysis. States hate nothing more than losing their exclusive copyright on intelligence.
To understand why this panic is misplaced, look at how deepfakes are actually used in criminal enterprises. They are primarily tools of financial fraud, not geopolitical destabilization. A scammer does not need to overthrow a government when they can trick a mid-level corporate accountant into wiring fifty million dollars via a simulated video call. Conflating financial scams with existential state collapse is a convenient way for law enforcement to secure more emergency powers for problems that require standard police work, not martial law or algorithmic censorship.
The Real Vulnerability
If machine learning is not the existential boogeyman keeping security chiefs awake at night, where does the real danger lie?
It lies in institutional over-reliance on brittle automated systems for critical infrastructure.
Governments and financial institutions are rushing to integrate probabilistic software into power grids, traffic routing, and border control because they are terrified of falling behind their geopolitical rivals. This is where the danger creeps in. Not because the software is malicious, but because it is frequently misunderstood by the humans who deploy it.
When you wire a black-box predictive model into a municipal water supply or a stock exchange clearing house, you introduce systemic fragility. The system does not need to hate you to crash your economy; it just needs to encounter a statistical anomaly outside its training distribution and fail silently while operators assume it knows what it is doing.
I have seen financial institutions lose millions because an automated risk management model optimized for a bull market encountered a liquidity crunch and doubled down on failing positions because nobody in the boardroom understood the weights inside the neural network. The threat is not rebellion. It is catastrophic incompetence disguised as efficiency.
How to Fix the Security Paradigm
If we want to secure our digital borders without choking economic vitality, we have to stop treating algorithms like foreign agents.
First, shift the focus from content moderation to cryptographic verification. Trying to stop the generation of synthetic media or unauthorized code through state censorship is like trying to bail out the ocean with a teaspoon. Instead, build verifiable provenance chains for digital assets. If every official communication, financial transaction, and public broadcast carries a cryptographic signature proving human origin, deepfakes instantly lose their disruptive edge in the public sphere.
Second, audit the infrastructure, not the models. Regulators love to debate ethics boards and open-source licensing restrictions while ignoring the physical supply chain of silicon and energy. The real geopolitical choke point is not an algorithm file on GitHub; it is the fabrication plants producing advanced semiconductors and the power plants keeping server farms cool. Securing a nation means protecting physical supply chains, not criminalizing math.
Finally, stop pretending that law enforcement agencies can regulate code faster than the market writes it. Every hour spent drafting bureaucratic compliance frameworks for neural networks is an hour wasted on securing actual network perimeters against human adversaries who are simply using better calculators.
The next time an official stands behind a podium warning that software is about to dismantle the state, check what budget they are trying to pass. The computer is not coming for your security clearance. The people panicking about it are just trying to hide their own obsolescence.